
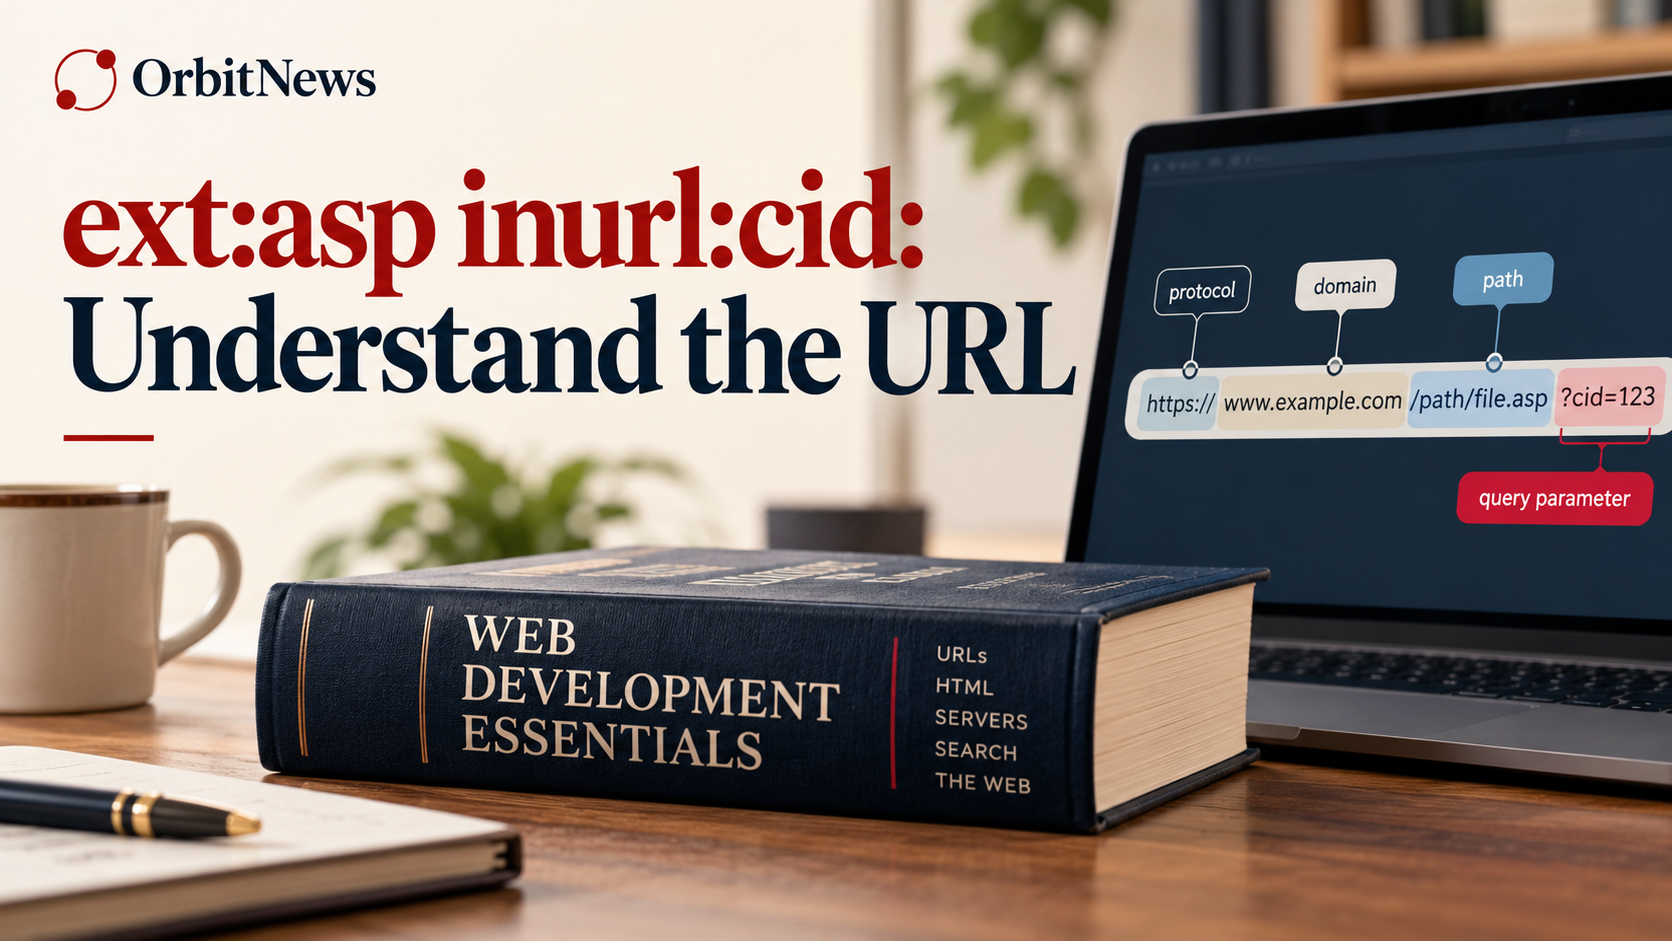
ext:asp inurl:cid is a search expression intended to combine an ASP-related extension condition with cid in a web address. It does not expose a site’s server-side source code, explain every parameter, or prove that an application has a security flaw.
To interpret it usefully, separate the visible address from the response a server sends and the code that produced that response. Those are different parts of a web application. A naming pattern can help discovery, but it cannot replace documentation or an authorised technical review.

Breaking down ext:asp inurl:cid
Operator lists commonly describe ext: as an extension-related filter and inurl: as a URL-term condition. Google’s current general help documents filetype: and Advanced Search, but it does not comprehensively guarantee every legacy ext: combination. Do not promise that ext:asp will return a complete inventory of ASP pages.
The cid portion is simply a label to investigate. It might appear in a path, a parameter name, or another part of an address. It has no universal meaning across all applications, and a short label is not enough to establish the type of record it refers to.
An invented example is https://example.com/view.asp?cid=42. The path ends with .asp and the query string contains cid with the value 42. This example illustrates an address structure only; it is not a live target or evidence about a database behind any actual website.
What an ASP page tells the browser
Microsoft’s IIS documentation describes Classic ASP as a server-side scripting environment for dynamic pages. The server processes the application and sends a response to the browser. Seeing .asp in an address is not equivalent to receiving the underlying server-side programme.
Classic ASP and technologies described as ASP.NET should also be identified carefully rather than treated as one interchangeable label. This article does not provide an installation guide or claim that an old deployment procedure is appropriate for a current server. Consult the documentation relevant to the actual application and environment.
A website can also use routing or other address conventions that do not reveal implementation details plainly. The absence of .asp does not prove the absence of a particular server technology. Likewise, a familiar suffix alone does not establish an application’s version, maintenance status, or security posture.
Filename, response format and source code are different
An address ending in .asp can return an HTML document. Google’s indexing documentation explains that file type is primarily determined using the returned Content-Type header, with extensions or parsing used in some circumstances. A filename-related search should not therefore be described as a complete classification of application code.
The browser’s rendered page, its received HTML, and the server’s original scripts are separate things. A search result that points to a generated page does not automatically provide the files used to generate it. Keep this distinction clear when explaining what a query can reveal.
For a content audit, the question may simply be whether an older public page still serves the intended article. For a technology review, you need more evidence about the system itself. Do not answer the second question with a result gathered only for the first.
How to interpret cid responsibly
Look for an explanation in the application’s official documentation or authorised codebase. If no definition is available, describe cid as a parameter or address label without inventing its expansion. Common guesses are not proof of the meaning chosen by a particular developer.
For ordinary browsing, follow the website’s published navigation. Editing identifier values to explore unknown records is not necessary to understand the query. Public discoverability does not provide permission to access private accounts, enumerate personal data, or interfere with an application.
If you administer the website, use the appropriate internal documentation, route definitions, and content records. These can explain the parameter’s role much more reliably than a public search expression. Keep private configuration and personal information out of public audit notes.
Better searches for different goals
| Illustrative query | Purpose |
|---|---|
"Classic ASP" "URL parameters" | Learn the concepts without targeting an unknown application. |
site:learn.microsoft.com IIS Classic ASP | Locate Microsoft’s documentation for the technology. |
site:example.com inurl:cid | Explore a verified authorised domain’s public naming pattern. |
"exact page title" "publisher" | Recover a content page without relying on legacy extension syntax. |
The example.com domain is a placeholder. These patterns concern discovery and documentation, not exploitation or a claim that a particular system is insecure. Choose the query according to the evidence you actually need.
A practical approach for an authorised site audit
Start with the site’s own content inventory and known legacy addresses. Identify which public pages should remain, which have replacements, and which are no longer intended to serve content. Record the expected destination instead of judging an address by its suffix alone.
For indexing questions, inspect the relevant URL through Search Console where you have access. Google’s search-operator guidance explicitly describes retrieval and indexing limits. A missing public search result is not proof that an ASP page never existed or that the server is not using that technology.
If a page redirects, examine whether the destination answers the same user need. A migration can preserve a useful article under a cleaner address, while an unrelated landing page may not preserve the original content. Describe what you observed rather than assuming that every redirect is a successful replacement.
For related reading, see the related PHP-and-cid search expression and finding the right technical context.
Frequently asked questions
Does ext:asp inurl:cid reveal ASP source code?
No. A server-side ASP page normally sends a generated response. Its visible address does not automatically expose the original scripts.
Is cid always a category identifier?
No. Its meaning is application-specific. Use official documentation or authorised code to establish the definition.
Does a matching address prove a vulnerability?
No. An extension and a parameter name are not evidence of a security flaw. A finding requires appropriate supporting evidence.
Is the legacy ext: expression guaranteed to work consistently?
Google’s current general help does not comprehensively guarantee it. Use documented search methods and verify the results rather than promising completeness.
Sources
Microsoft: Classic ASP and server-side pages; Google: indexable file types; Google search-operator documentation; Google Advanced Search filters.
